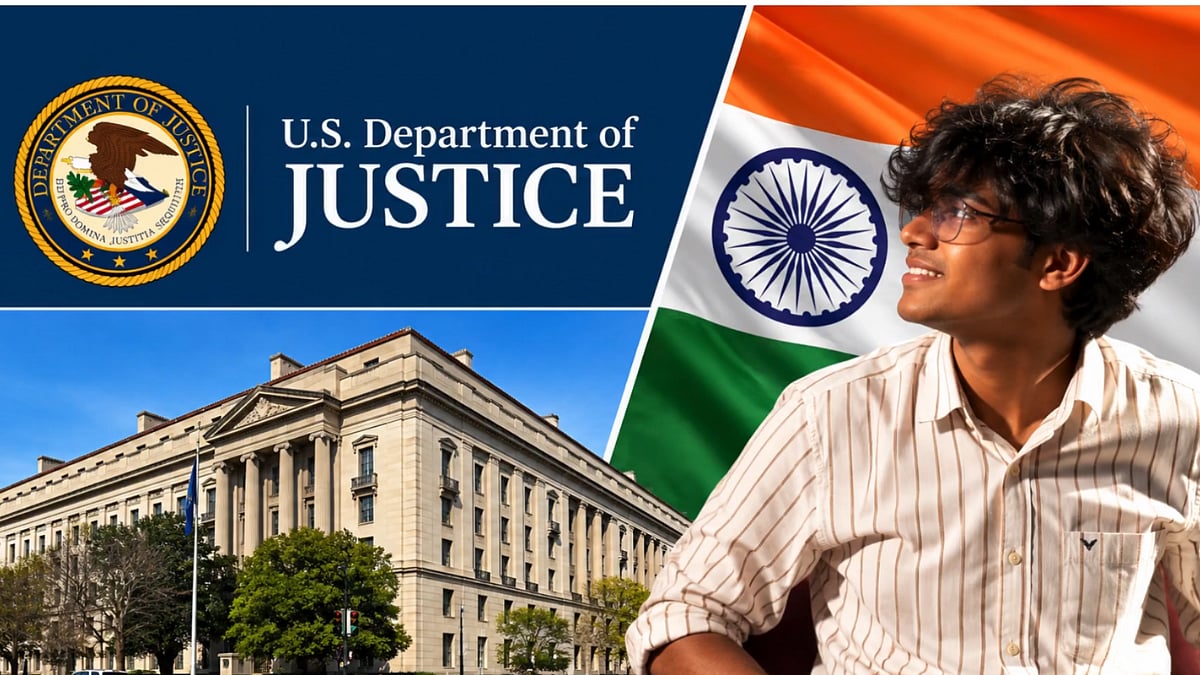
A 19-year-old Indian cybersecurity researcher has reportedly earned recognition from the US Department of Justice for responsibly disclosing a critical security flaw in one of its systems.
From CBSE OSM flaw to a US federal agency bug
According to multiple reports, Nisarga Adhikary, a self-taught researcher from Siliguri, West Bengal, and a threat intelligence engineer at IIT Kanpur's C3iHub, used custom scripts to identify a vulnerability in a DOJ law enforcement system roughly a week before it was patched. The department is said to have added his name to its public acknowledgements page under its Vulnerability Disclosure Policy (VDP), a framework that shields good-faith security researchers from legal action when they report flaws through proper channels.
A track record of responsible disclosure
This isn't Adhikary's first brush with high-profile vulnerability reporting. Earlier this year, he identified critical flaws in the security of CBSE's On-Screen Marking (OSM) portal including, he claimed, a master password stored in plain text that could bypass two-factor authentication. He reported the issues to India's CERT-In rather than exploiting them, a move that drew national attention and eventually led IIT Kanpur to hire him. Adhikary is also currently working with a US Department of Defense system.
A broader signal for ethical hacking
From flagging a national exam board's security gaps to reportedly being recognised by a US federal agency - it is evidence that young, independent researchers can meaningfully strengthen government cybersecurity when they work through legitimate disclosure channels rather than exploiting vulnerabilities for personal gain.